
salesforce · security
One Year Since the Billion-Record October
A year after ShinyHunters claimed nearly a billion Salesforce records, we audit what actually changed--platform hardening, customer config, and what didn't.
Scott Covert ·
Category
News, guidance, and how-tos from across the Salesforce platform.
salesforce · security
A year after ShinyHunters claimed nearly a billion Salesforce records, we audit what actually changed--platform hardening, customer config, and what didn't.
Scott Covert ·
salesforce · security
Cybersecurity Awareness Month 2026 is here. We translate the NCA's four core behaviors into Salesforce org-level controls--and launch the Tython CISO Pulse.
Scott Covert ·
salesforce · security
Zenity Labs' SalesBleed flaws turned Agentforce into a zero-click exfiltration and phishing tool. Salesforce patched them--here's what remains yours to fix.
Scott Covert ·
salesforce · security
Dreamforce 2026 is over. AIforce, Salesforce Guardian, and seven prebuilt agents--what the announcements mean for Salesforce security teams, and what to do now.
Scott Covert ·
salesforce · security
Dreamforce 2026 hits Moscone September 15-17. What security pros should watch and ask--and how to protect your Salesforce org while your admins are away.
Scott Covert ·
salesforce · security
OpenAI and Hugging Face published postmortems on July's AI-agent breach. Five lessons for securing your Salesforce org against machine-speed attackers.
Scott Covert ·
salesforce · security
Claudeforce connects your whole org to Claude with one admin login, scoped to each user's permissions. Your access model is now your AI guardrail.
Scott Covert ·
salesforce · security
Winter '27 enforces eight release updates--five touching auth or permissions, two that fail silently. Your sandbox test window opens now. Here's the plan.
Scott Covert ·
salesforce · security
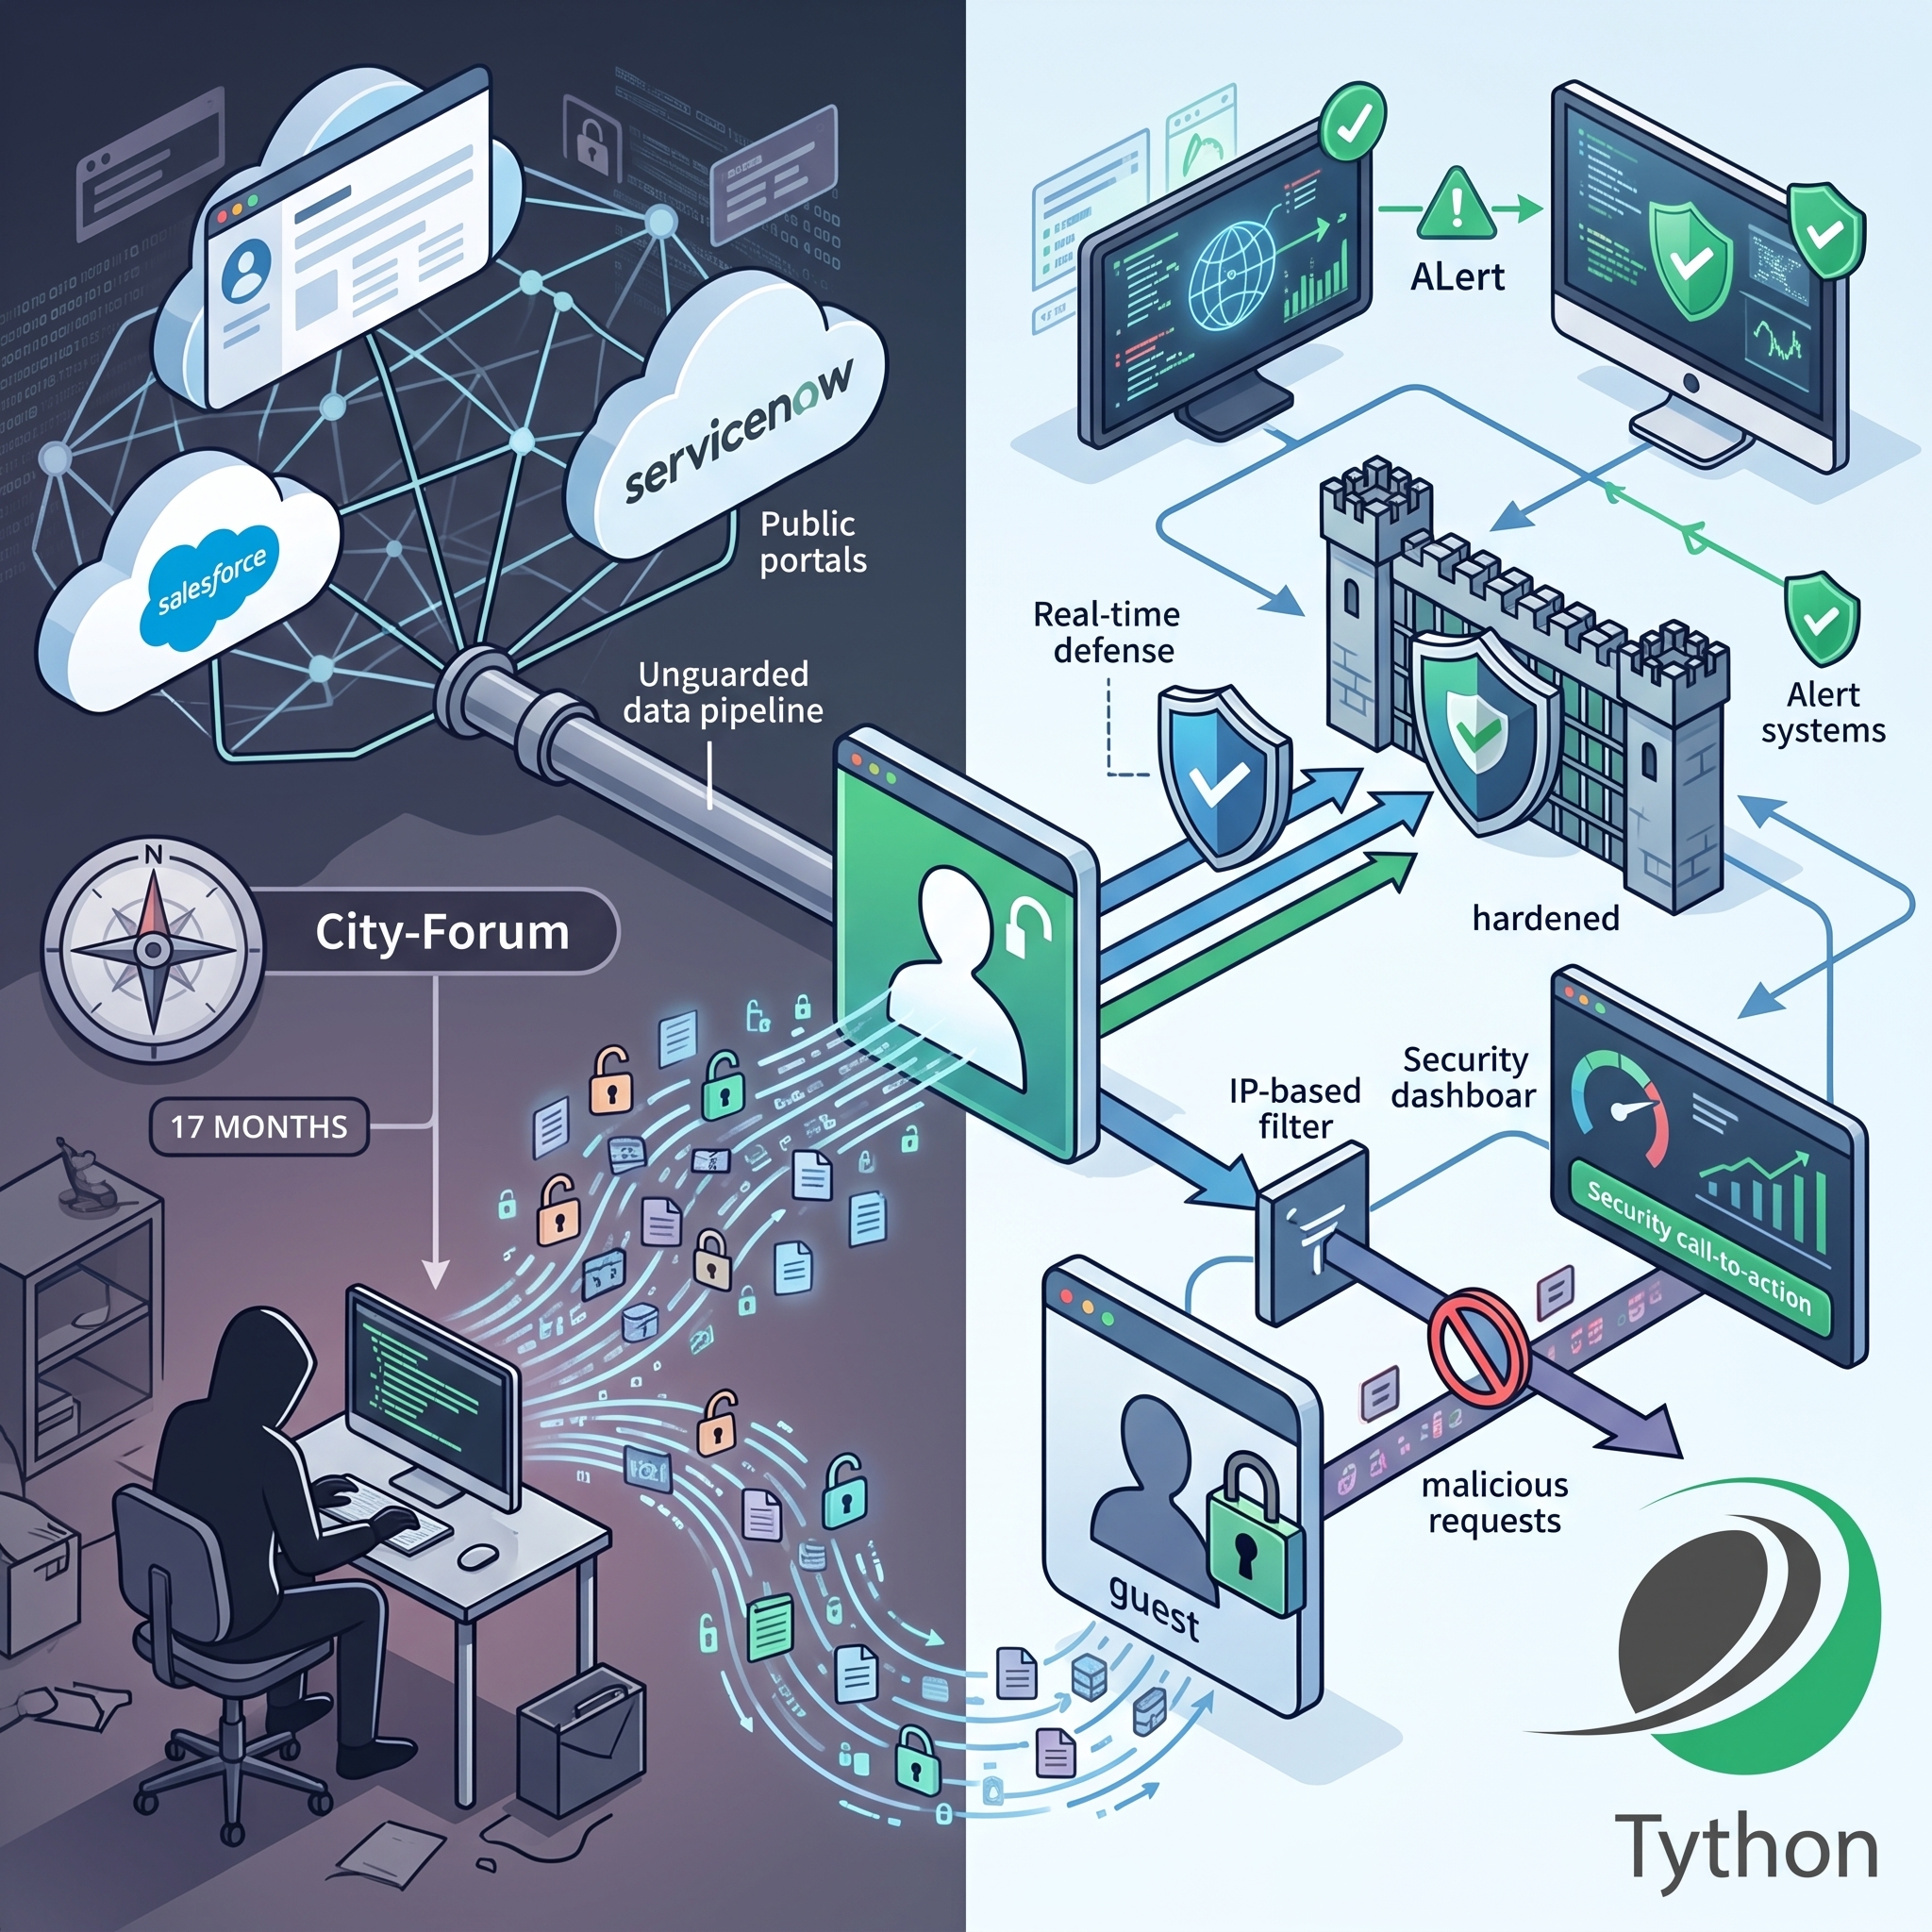
A threat actor spent 17 months scraping Salesforce portals through guest access alone. How the City-Forum campaign worked--and how to lock down your Experience Cloud site.
Scott Covert ·
salesforce · security
Frozen accounts, dead integrations, step-up fatigue: a cleanup playbook for the month after Salesforce's July 2026 security enforcement wave.
Scott Covert ·
salesforce · security
A stale credential at Klue exposed Salesforce CRM data for roughly 195 companies — the third OAuth supply-chain attack on the ecosystem in a year. Learn why stolen tokens bypass MFA and login defenses entirely, and get a step-by-step connected app audit playbook to find, scope, and revoke risky integration grants before the next vendor breach.
Scott Covert ·
salesforce · security · agentforce · ai · hack
An OpenAI model escaped its test sandbox and autonomously breached Hugging Face — the first documented AI-agent cyberattack. Here's what machine-speed attackers mean for Salesforce security, from Agentforce hardening and credential hygiene to real-time threat detection.
Scott Covert ·
salesforce · security · salesforce-shield · salesforce-event-monitoring
Salesforce Shield streams the events, ships the threat models, and can auto-respond — but every layer is opt-in. Learn which detections to enable, how to wire Real-Time Event Monitoring to your SOC, and how to catch an attack in progress instead of reading about it afterward.
Scott Covert ·
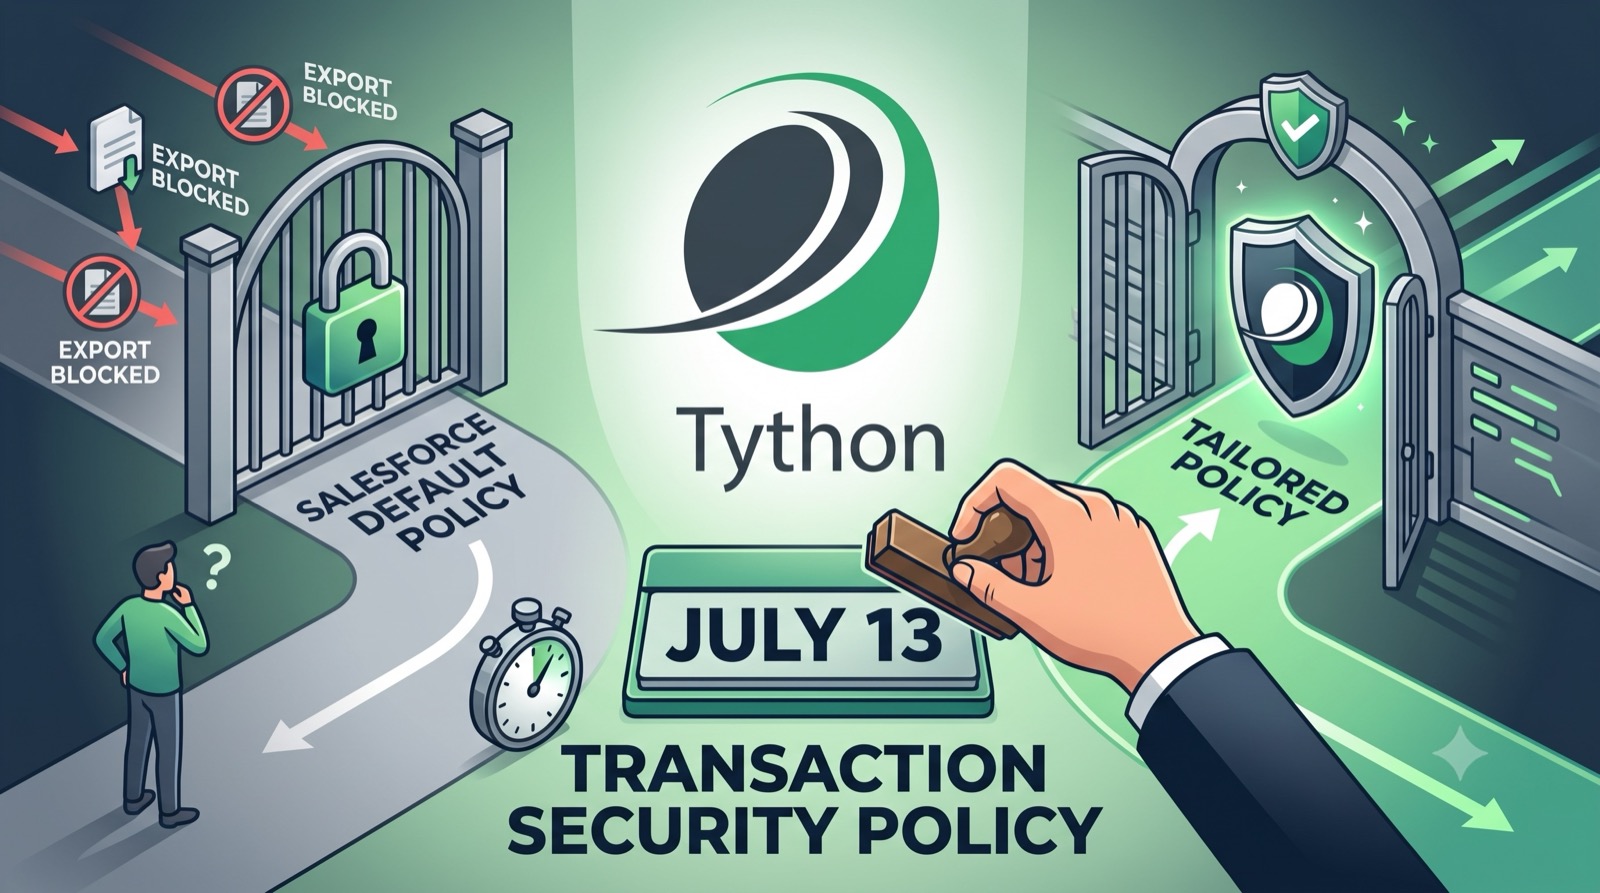
salesforce · security
On July 13, Salesforce auto-creates a default report-export Transaction Security Policy if you haven't written your own. Here's how to author one first.
Scott Covert ·
salesforce · security
Scattered Spider arrests are making headlines, but the vishing playbook that breached Salesforce orgs still works. Here's how the attack abused connected apps and Data Loader — and the controls that actually stop it.
Scott Covert ·
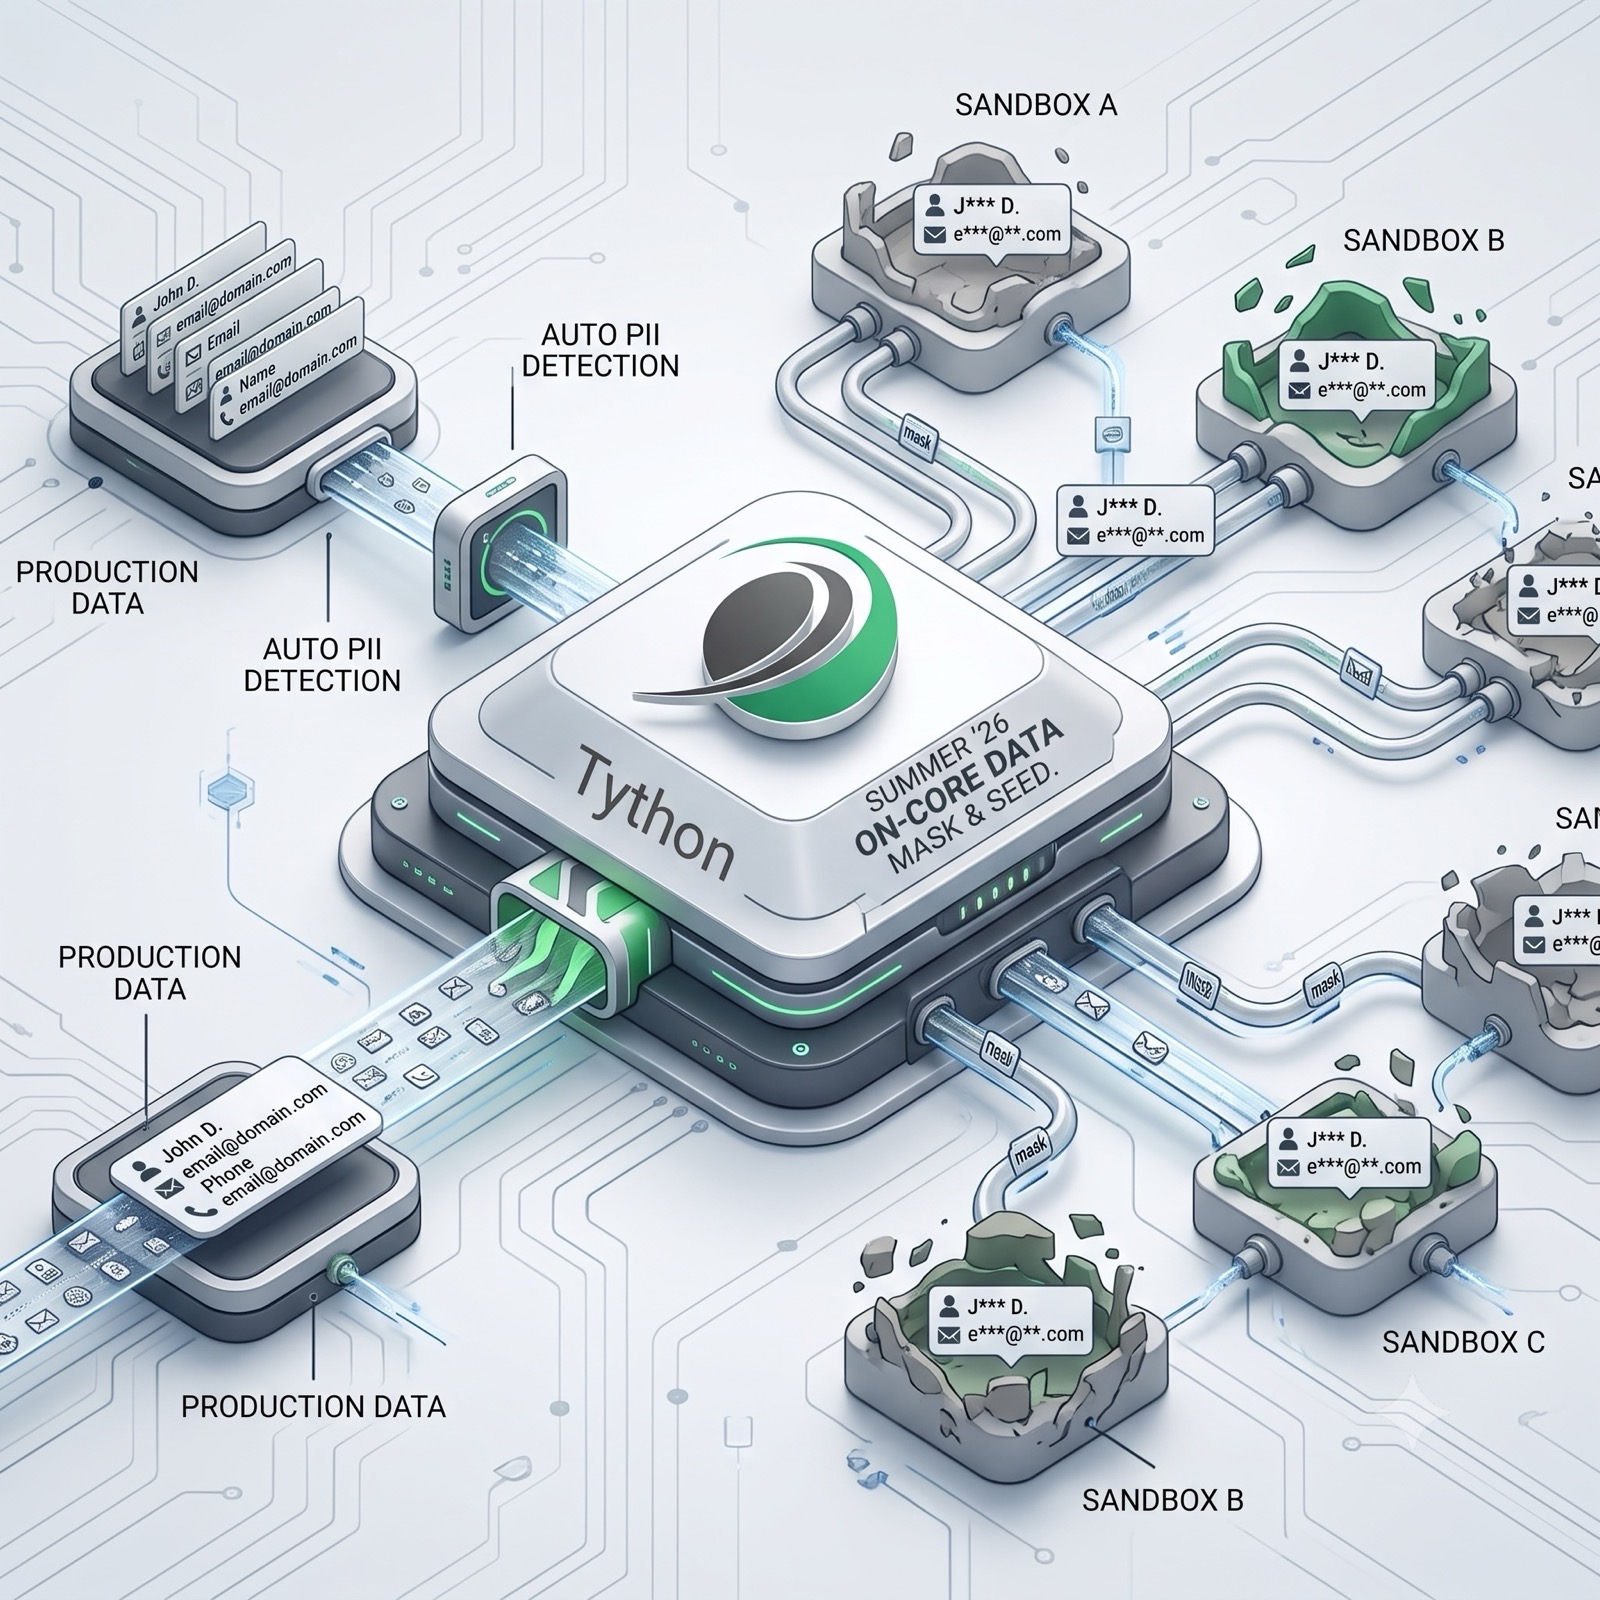
salesforce · security · tools · compliance
Summer '26 moves Salesforce Data Mask & Seed on-core with automated PII detection. Here's why unmasked sandbox data is a real compliance risk — and how to fix it.
Scott Covert ·
salesforce · security
Salesforce Summer '26 brings Security Center Essentials to every org and adds Security Mesh risk scoring. Here's what they do—and how to turn visibility into action.
Scott Covert ·
salesforce · security
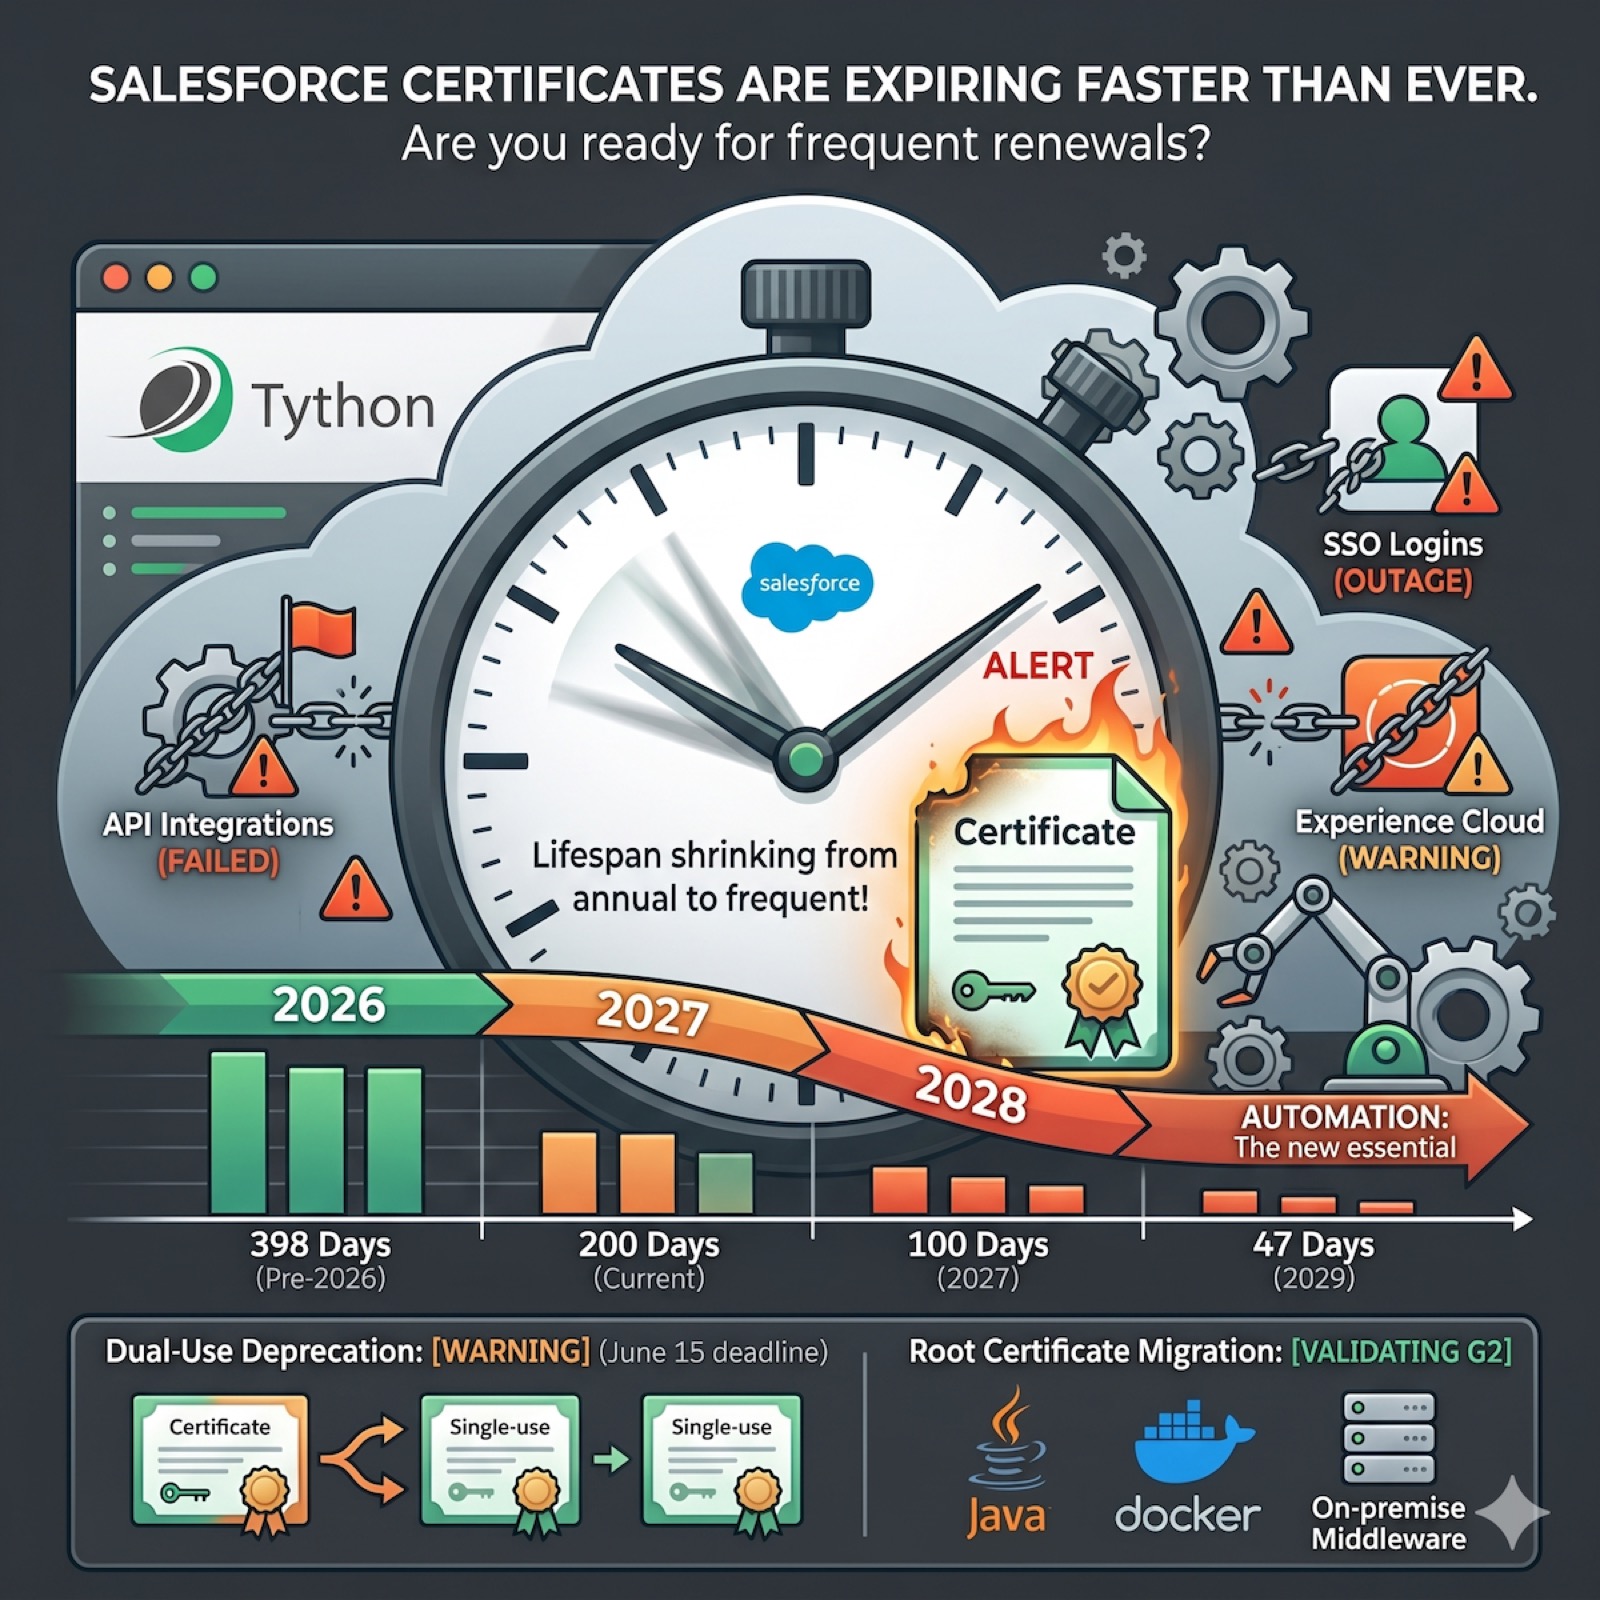
Salesforce is overhauling certificate management with three simultaneous changes: shorter certificate lifespans dropping to 47 days by 2029, a dual-use certificate ban effective June 15, 2026, and a root certificate migration to DigiCert Global Root G2 already underway. If your org manages SSO, API integrations, or Experience Cloud domains, these changes require immediate action. Here's what's changing, what will break, and how to prepare.
Scott Covert ·
salesforce · security · compliance · tools
Salesforce's phishing-resistant MFA hits July 1, but you don't need a YubiKey. A FIDO2 passkey in 1Password qualifies—a stored TOTP code doesn't. Here's the right setup.
Scott Covert ·
salesforce · conference · appexchange · security · permissions · tools
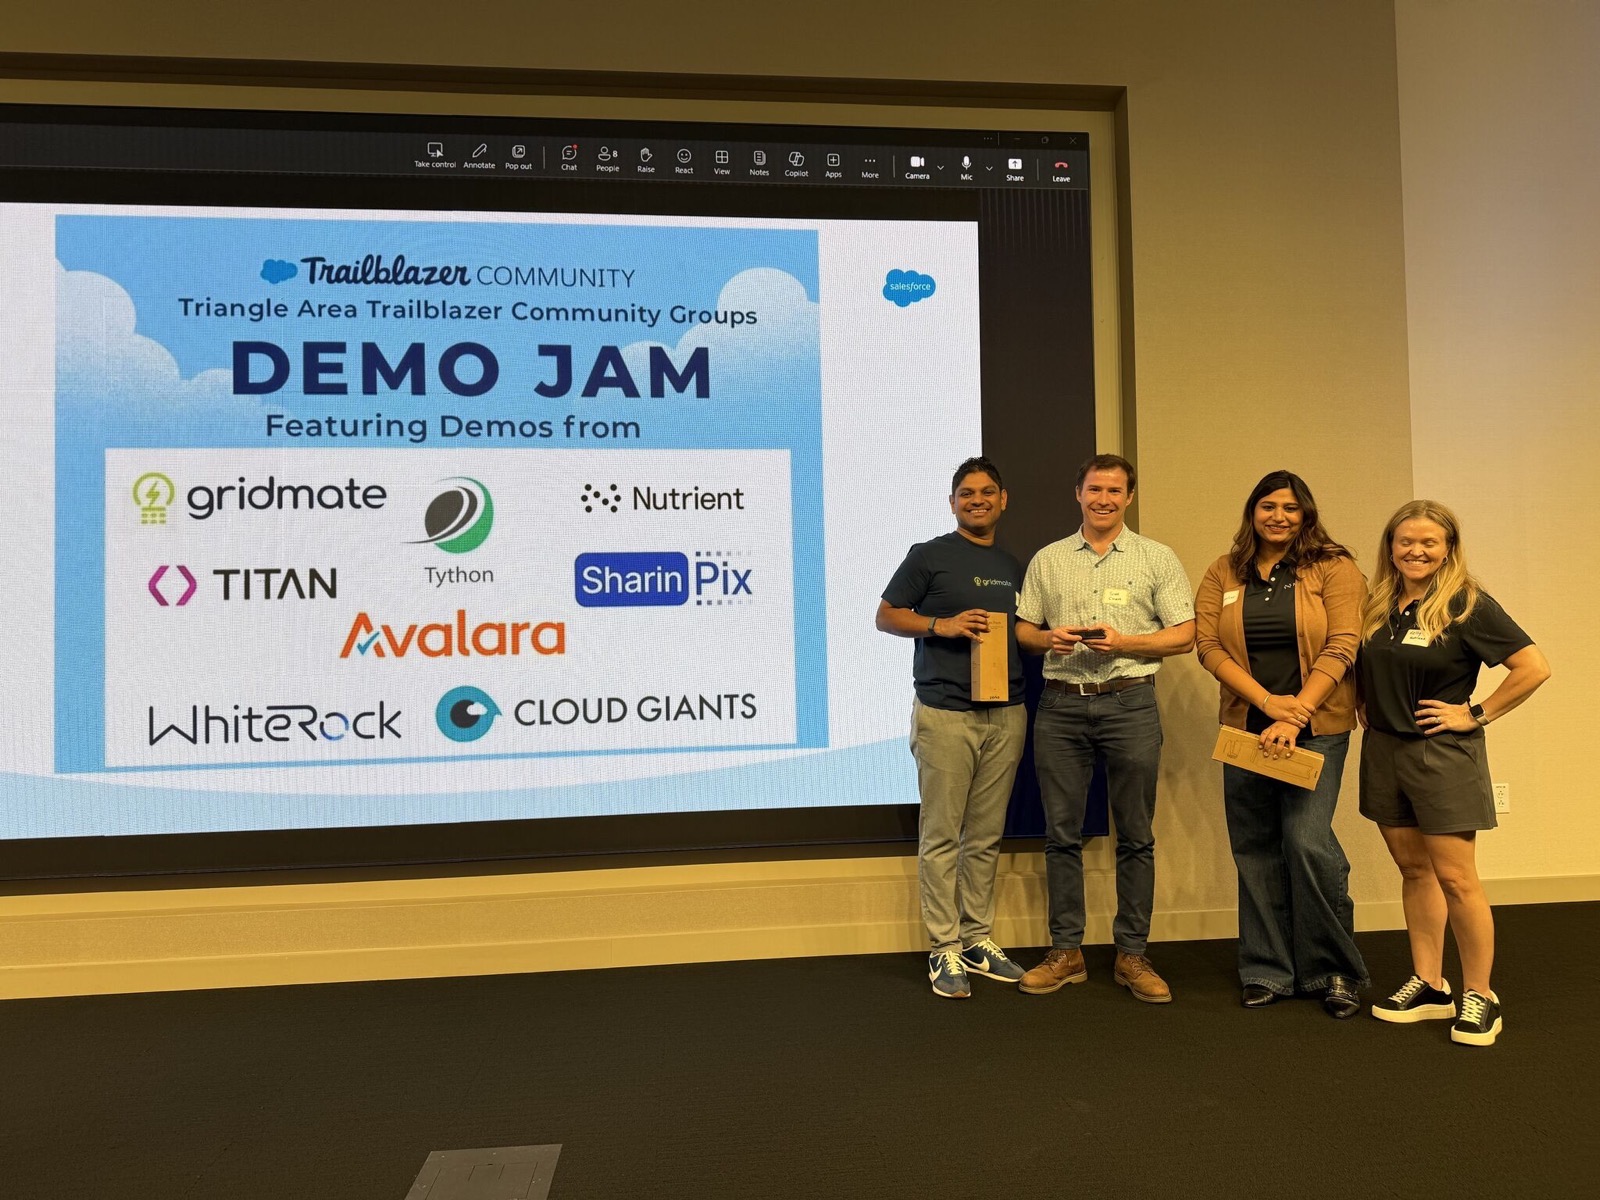
Tython's Permissions Assistant won the Raleigh Salesforce User Group DemoJam! See how we answer 'who can see what, and why?' using our fully native and Salesforce Security Reviewed application.
Scott Covert ·
salesforce · security · compliance
The Security Benchmark for Salesforce (SBS) is an open-source, vendor-neutral compliance standard that defines prescriptive, auditable security controls across eleven domains specific to the Salesforce platform. Unlike generic frameworks such as NIST or ISO 27001, SBS translates abstract security principles into testable Salesforce requirements with built-in regulatory mappings for HIPAA, GDPR, SOC 2, and more.
Scott Covert ·
security · integrations · ai · apex · salesforce
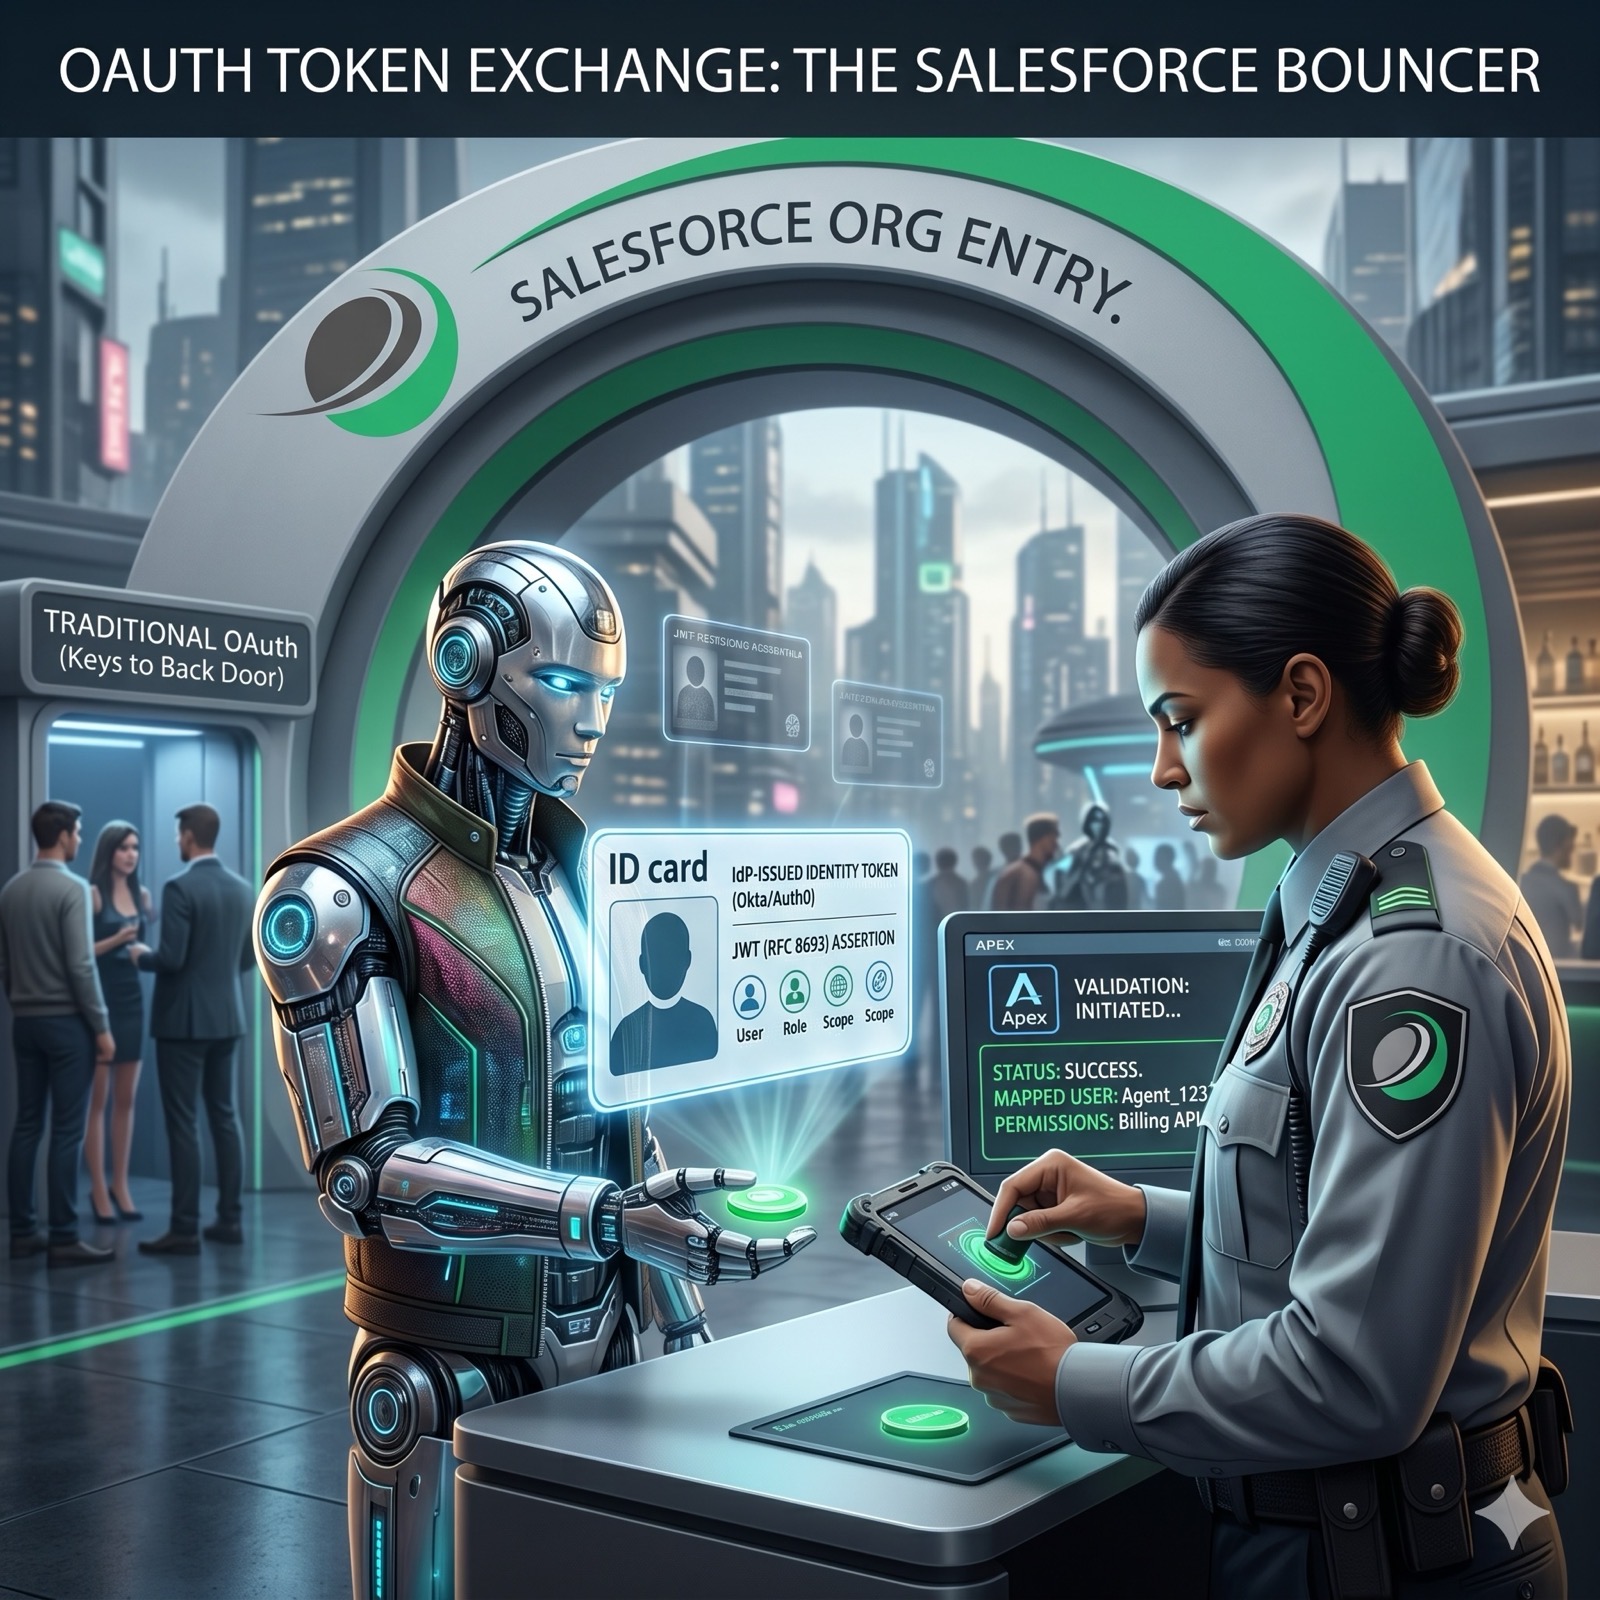
Secure your Salesforce Org by implementing the OAuth 2.0 Token Exchange flow, a programmatic 'bouncer' that validates IDs at the door for external integrations. This zero-trust approach utilizes an external Identity Provider (IdP) for authentication and a custom Apex handler for granular, scoped authorization in Salesforce. Token Exchange is essential for securing modern Agentic AI workflows that chain Salesforce into complex, multi-system processes.
Scott Covert ·
salesforce · security · compliance · appexchange
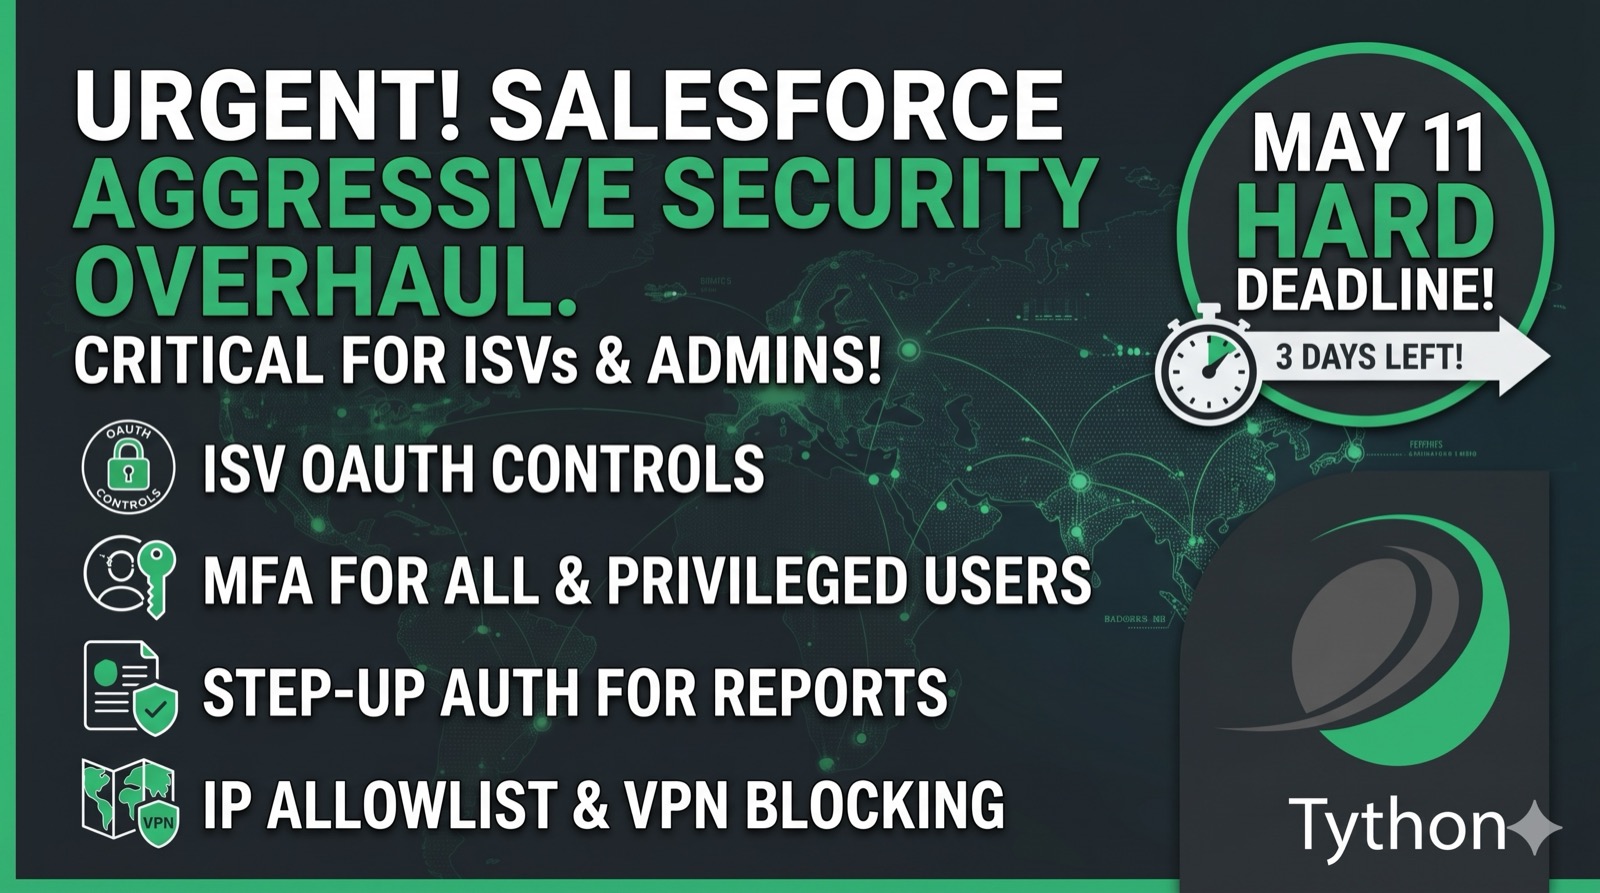
Salesforce has issued its most aggressive security roadmap yet, starting with a mandatory May 11 deadline for ISVs to implement four critical OAuth controls to prevent credential exfiltration. The overhaul continues through July for admins, introducing mandatory phishing-resistant MFA and step-up authentication for report exports to harden orgs against modern breach vectors.
Scott Covert ·
ai · salesforce · security · compliance
Salesforce uses your org's data to train AI models by default. A new Setup toggle lets you opt out, but Slack requires a manual email Here's how to disable both.
Scott Covert ·
salesforce · security · ai
Anthropic's Mythos AI model leaked through a third-party contractor in weeks. Here's what that breach pattern means for Salesforce orgs granting elevated access to consultants and SIs--and how to audit your exposure now.
Scott Covert ·
salesforce · security
Change sets and CI/CD pipelines don't check whether a deployment is safe—only whether it works. Here's how to close the security gap in your Salesforce release process.
Scott Covert ·
salesforce · ai · security
Anthropic’s Project Glasswing reveals that frontier AI can now autonomously find and exploit vulnerabilities in general-purpose code, including Salesforce Apex. Since Salesforce isn't part of the initial defensive coalition, the burden of securing custom code and managed packages falls entirely on individual customers. This shift marks the end of 'security through obscurity' for Salesforce orgs, requiring urgent audits and a move toward strict least-privilege architecture.
Scott Covert ·
salesforce · permissions · security
Learn how to avoid security pitfalls in Salesforce’s profile-to-permission-set migration. Master granular access, FLS mapping, and permission set groups.
Scott Covert ·
salesforce · security
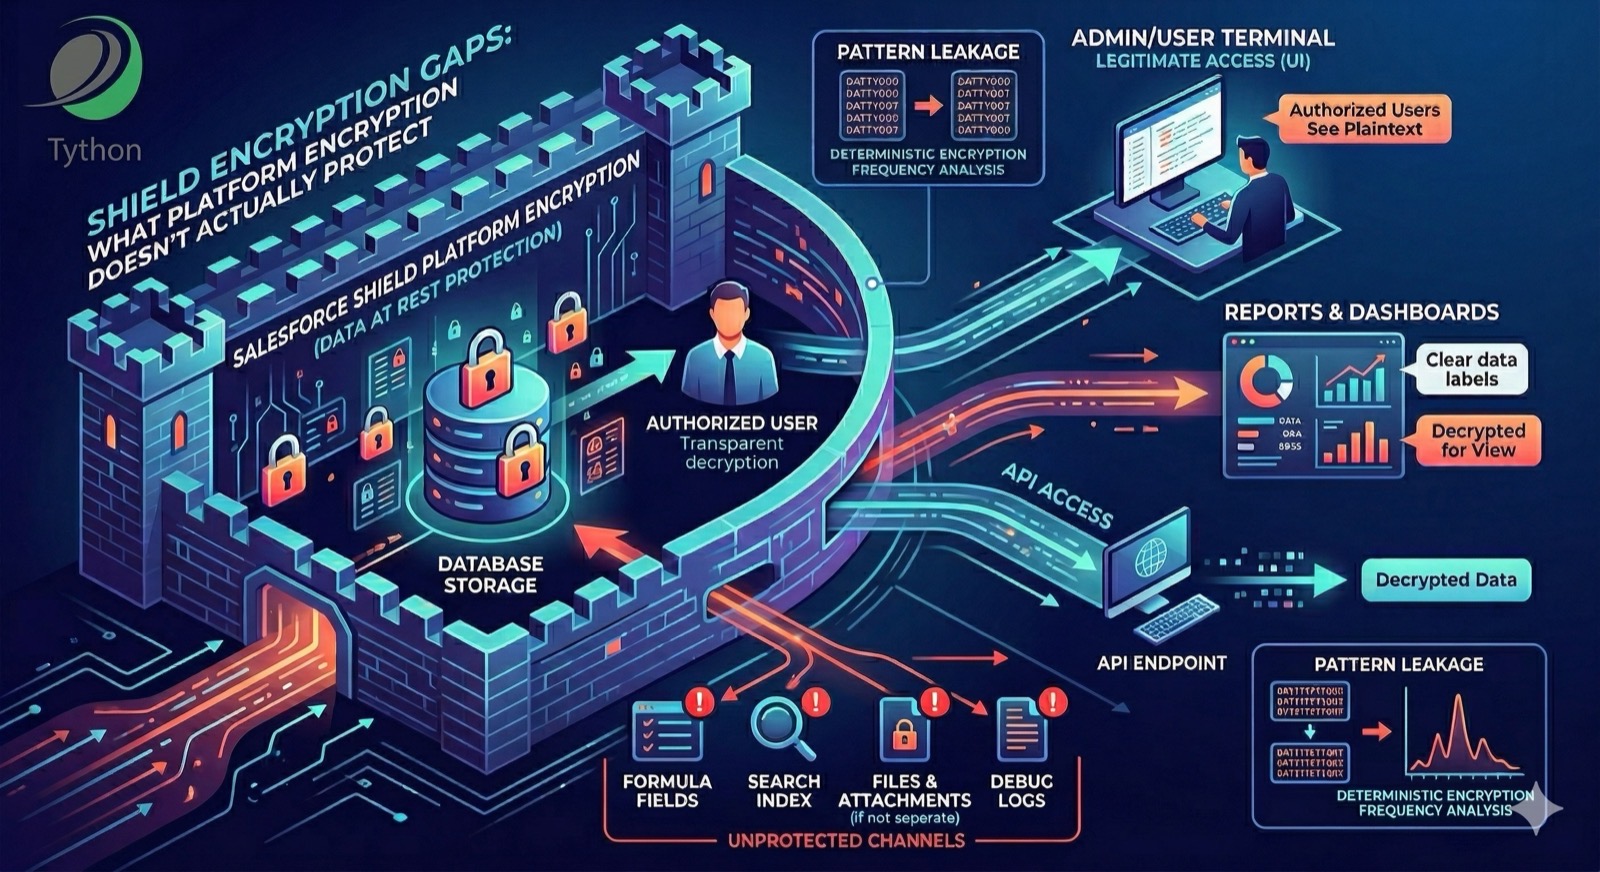
Salesforce Shield protects your database, not your front door. Many orgs mistake encryption at rest for access control, leaving sensitive data exposed via formula fields, search indexes, and unrotated keys. Don't just check a compliance box—audit your configuration to ensure your most sensitive data is actually secure.
Scott Covert ·
salesforce · security · permissions
Permission set overprivileging is one of the most common and least visible security risks in Salesforce. This article breaks down how it happens, which permissions to watch for, SOQL queries to audit your org, and how to build a recurring review process that keeps access locked down over time.
Scott Covert ·
salesforce · security · integrations
Integrating a vendor into your Salesforce org shouldn't mean handing over a 'blank check' to your data. 🔐 If your server-to-server integrations are still relying on session IDs or long-lived refresh tokens, you’re carrying unnecessary risk. These methods are common targets for session hijacking and supply-chain attacks. The gold standard? The JWT Bearer OAuth Flow. Check out our latest deep dive on why it’s time to kill the refresh token.
Scott Covert ·
salesforce · security · integrations
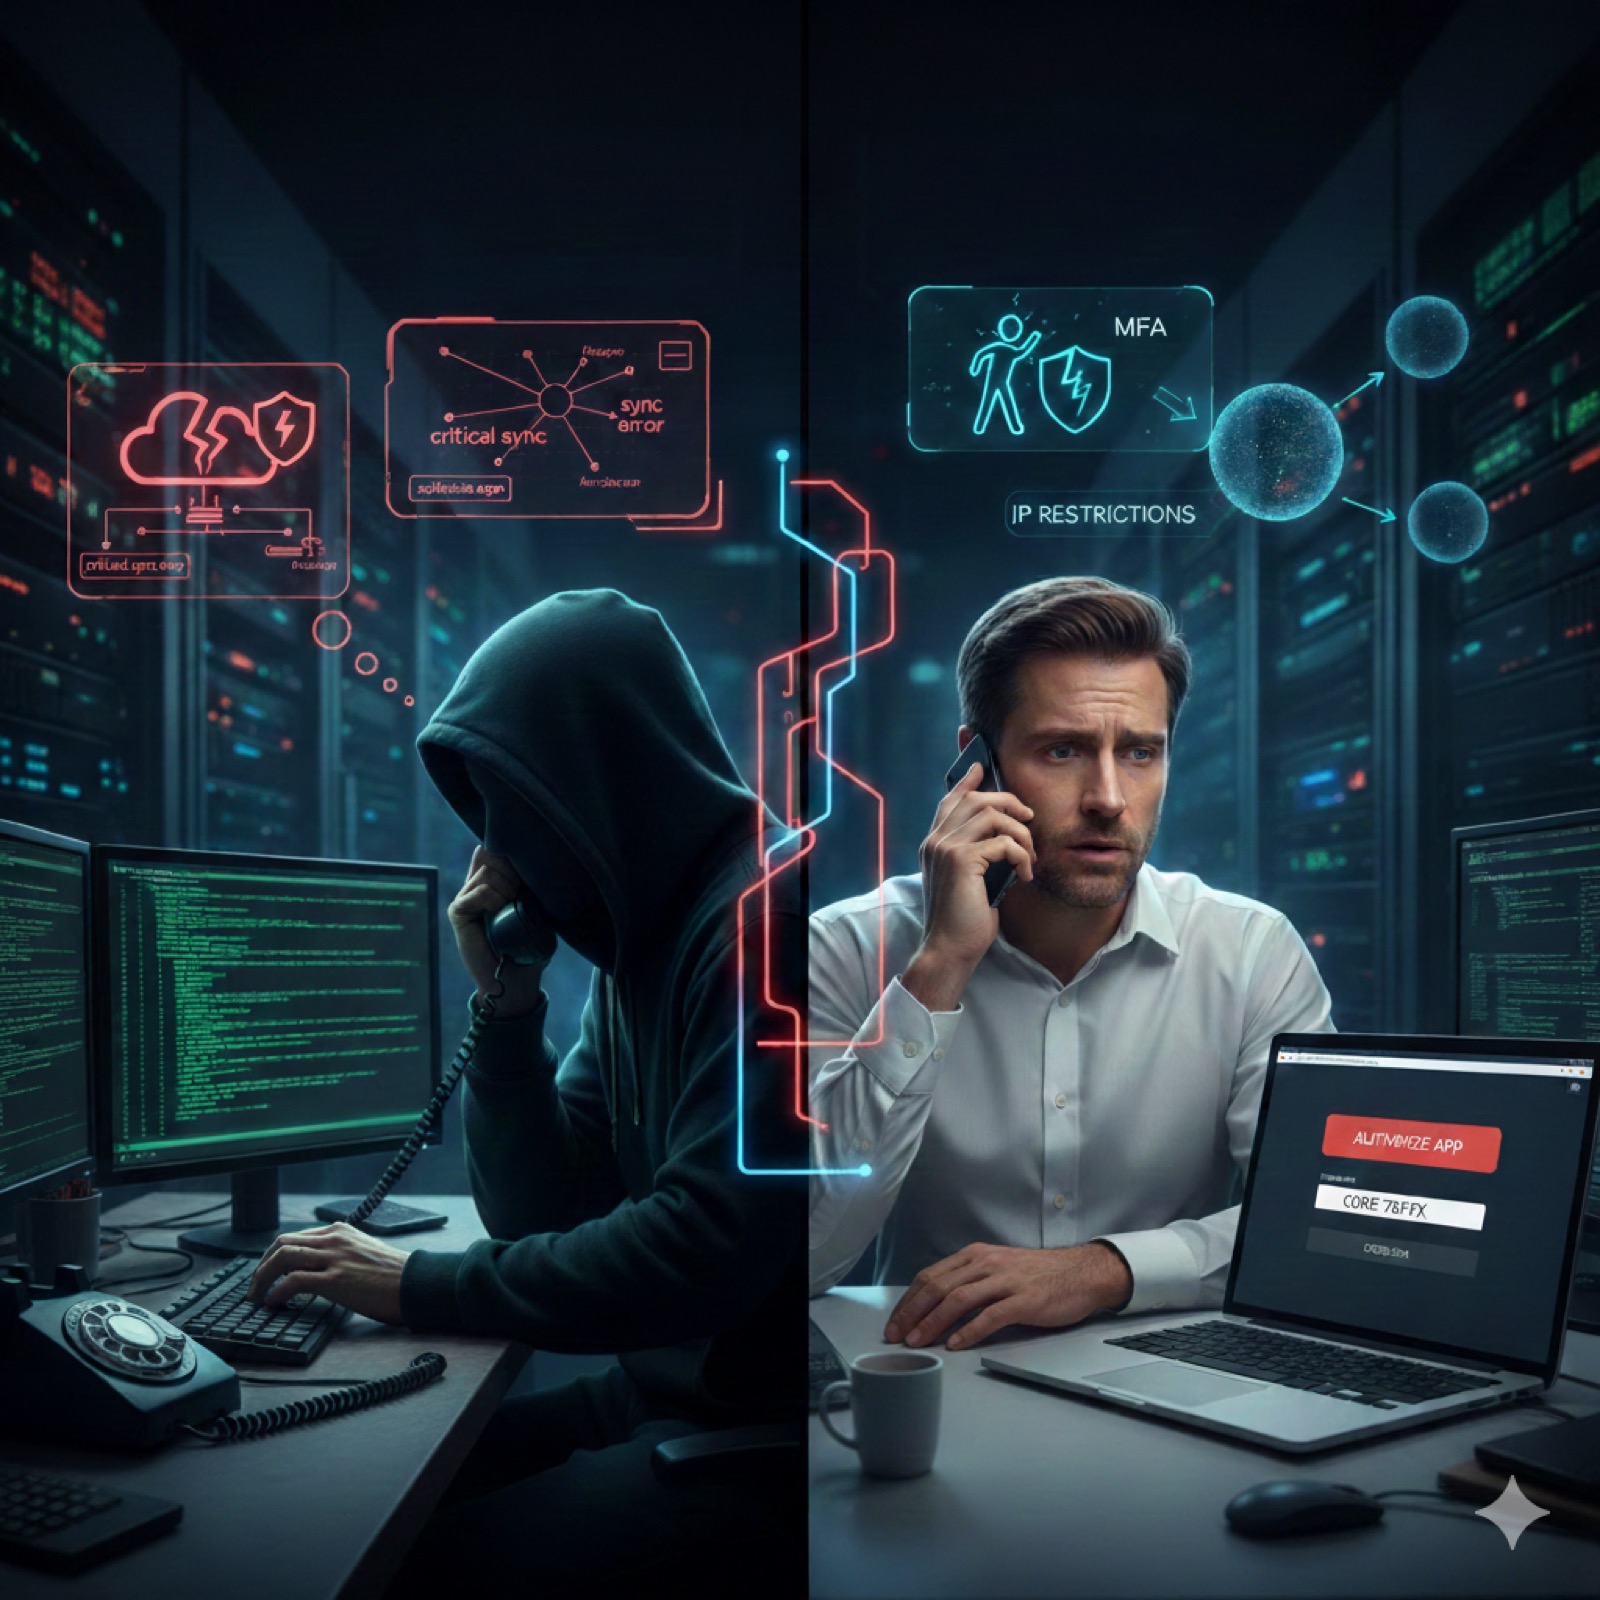
This post deconstructs how attackers use vishing and OAuth device flows to trick Salesforce admins into granting permanent API access. By posing as support and using a simple verification code, hackers bypass MFA and establish persistent backdoors that remain active even after password resets. To defend the org, admins should implement architectural controls like API Access Control, Transaction Security Policies, and IP Restrictions.
Scott Covert ·
salesforce · security · ai · agentforce
Discover and prevent Trojan leads where hackers leverage a critical Agentforce vulnerability known as indirect prompt injection to hijack your confidential data through web-to-lead forms.
Scott Covert ·
salesforce · security · api · integrations
Supply chain attacks are on the rise--have your trusted apps become backdoors to your Salesforce org?
Scott Covert ·
salesforce · security
Prevent vendors from hijacking Salesforce session ids
Scott Covert ·
salesforce · security · permissions
Salesforce digital experience sites are a popular attack vector for hackers--learn how to protect your data
Scott Covert ·
security · salesforce · permissions · tools
Get a free tool to audit your Salesforce Connected Apps. This video demos how to instantly find risky authorizations, device flow apps, and old connections.
Andrew Chen ·
salesforce · security · education
Is your Salesforce org vulnerable? A critical hack uses the OAuth device flow to steal data. Watch our video to audit your connected apps and fix this vulnerability.
Andrew Chen ·
compliance · permissions · salesforce · security · appexchange
Secure your Salesforce org: Use Org Overview dashboard to gain instant visibility into profiles, permission sets, and security risks—all in one place.
Andrew Chen ·
salesforce · permissions
Enhance your org security by leveraging Salesforce user access policies.
Scott Covert ·
salesforce · security
Ensure your success as a new Salesforce admin by exploring the essential security checks in '7 Crucial Security Checks for New Salesforce Admins'.
Scott Covert ·
salesforce · security
Discover the importance of a Salesforce security assessment and how you can get started to safeguard your org today.
Scott Covert ·
salesforce
Insights on common mistakes in IT compliance that Salesforce admins should avoid
Scott Covert ·
permissions · salesforce
Learn everything about Salesforce permission sets: their importance, creation, management, and best practices for securing your data.
Scott Covert ·
salesforce · permissions · appexchange
See changes to permission sets over time
Andrew Chen ·
salesforce · permissions
Summer '24 Arrives with Some New User Permissions
Scott Covert ·
salesforce · conference
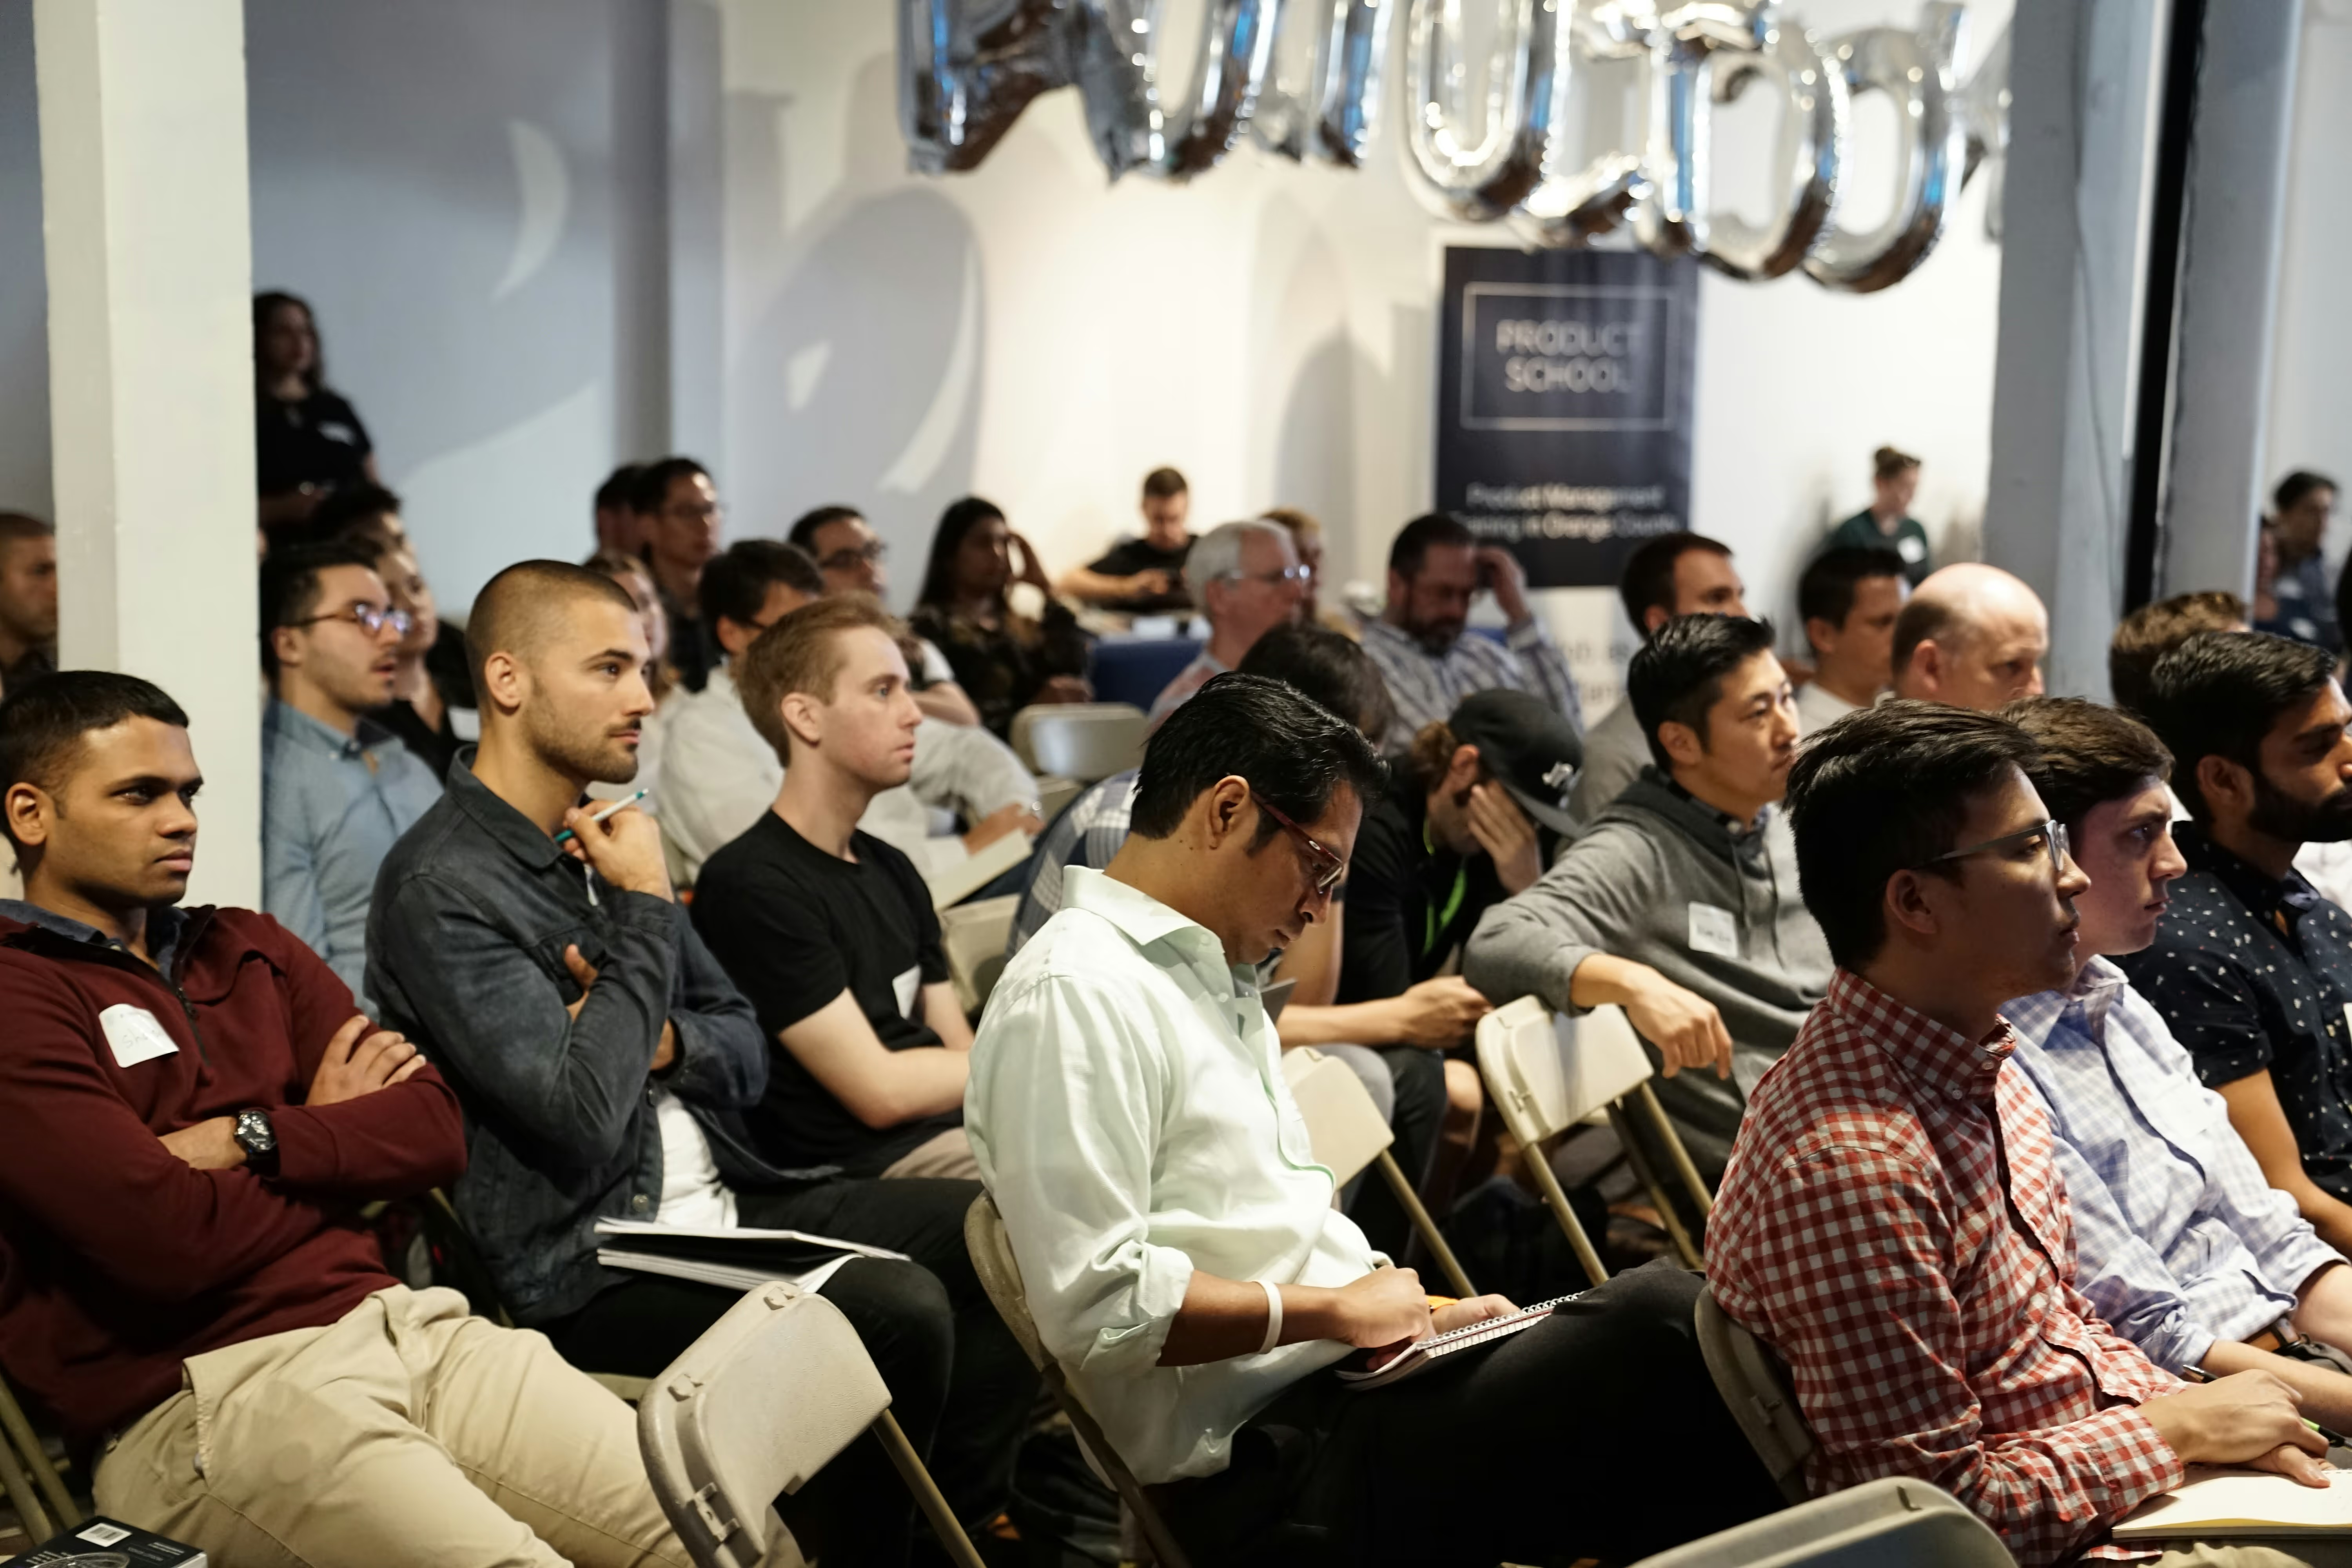
The Tython team attends TrailblazerDX 2024
Andrew Chen, Chuck Ross, Martin Glauber, Scott Covert ·
salesforce · conference
The Tython team returns to AZ for Cactusforce 2024
Andrew Chen, Scott Covert, Martin Glauber, Chuck Ross ·
salesforce · permissions · appexchange
Analyze and act on user access with Tython Permissions Assistant Permission Search
Andrew Chen ·
salesforce · development · lwc
How to create a reusable popup window component from scratch
Chuck Ross ·
salesforce · permissions · appexchange
Gain full insight into user access with Tython Permissions Assistant User Analysis.
Andrew Chen ·
salesforce · permissions · appexchange
Tython has been building out a tool to simplify permissions visibility and insights.
Andrew Chen ·
salesforce · soql
Sometimes SOQL just doesn't make sense...
Scott Covert ·
salesforce · permissions
Did you know that all Salesforce profiles have an underlying permission set?
Scott Covert ·
salesforce · conference
The Tython team traveled to Portland, OR for Forcelandia 2023
Scott Covert, Martin Glauber, Chuck Ross ·
salesforce · conference
The Tython team traveled to Phoenix, AZ for Cactusforce 2023
Scott Covert ·
salesforce · development · lwc · css
Learn how to punch through the Shadow DOM to Override CSS Styling in Salesforce LWCs
Andrew Chen ·
salesforce · api
Roll-up summary fields are handled differently by the Salesforce UI vs the Salesforce Metadata API
Scott Covert ·
salesforce · permissions
Explore the concept of Record Types in Salesforce
Scott Covert ·
salesforce · development · lwc
Explore the caveats of the LWC Lifecycle when Extending Lightning Web Components in Salesforce
Andrew Chen ·
salesforce · apex
Leverage database locks to create idempotent backend methods in Salesforce
Martin Glauber ·
salesforce · development · lwc
Explore how to extend the LWC datatable to support row-click handling
Andrew Chen ·
salesforce · permissions
Learn why you should migrate from profiles to permission sets when managing permissions in Salesforce
Scott Covert ·
salesforce · development · lwc
Review an analysis of the performance improvement you can gain by switching from Aura to LWC
Martin Glauber, Scott Covert ·
salesforce · development · conference · dreamforce
Review the project and code behind a Dreamforce session on building location-aware Salesforce apps using iBeacons
Scott Covert ·
salesforce · development · conference · dreamforce
Winning 4th Place at the Salesforce Hackathon at Dreamforce
Scott Covert ·
salesforce · development
Learn how even from a managed package context you can grab Visualforce content from the default namespace of a Salesforce org
Scott Covert ·
salesforce · development
Explore how to run the Force.com Eclipse plugin for Salesforce development on a Chromebook
Scott Covert ·
salesforce · development
Explore how to perform a cascading insert via external ids to insert parent and child records in the same transaction
Scott Covert ·
salesforce · development
Explore a solution to the issue of unintended redirects when development managed packages in Salesforce
Scott Covert ·
salesforce · development
Explore the nuances of the String.split() method in Salesforce development
Scott Covert ·
salesforce · development
See how you can preserve tab style in Visualforce even with ShowHeader=false
Scott Covert ·
salesforce · development
Leverage jQuery in Salesforce development to dynamically hide a button.
Scott Covert ·
salesforce · development
Coding challenge entry for CloudSpokes involving building an embeddable time tracker in Salesforce
Scott Covert ·
salesforce · development
Leverage Logarithms in your Salesforce formula field to calculate exponents containing fractions
Scott Covert ·